
Quick Facts
Introduction
Learn how AI agents plan tasks, use tools, inspect results and request approval, plus the main risks and a safe deployment checklist.
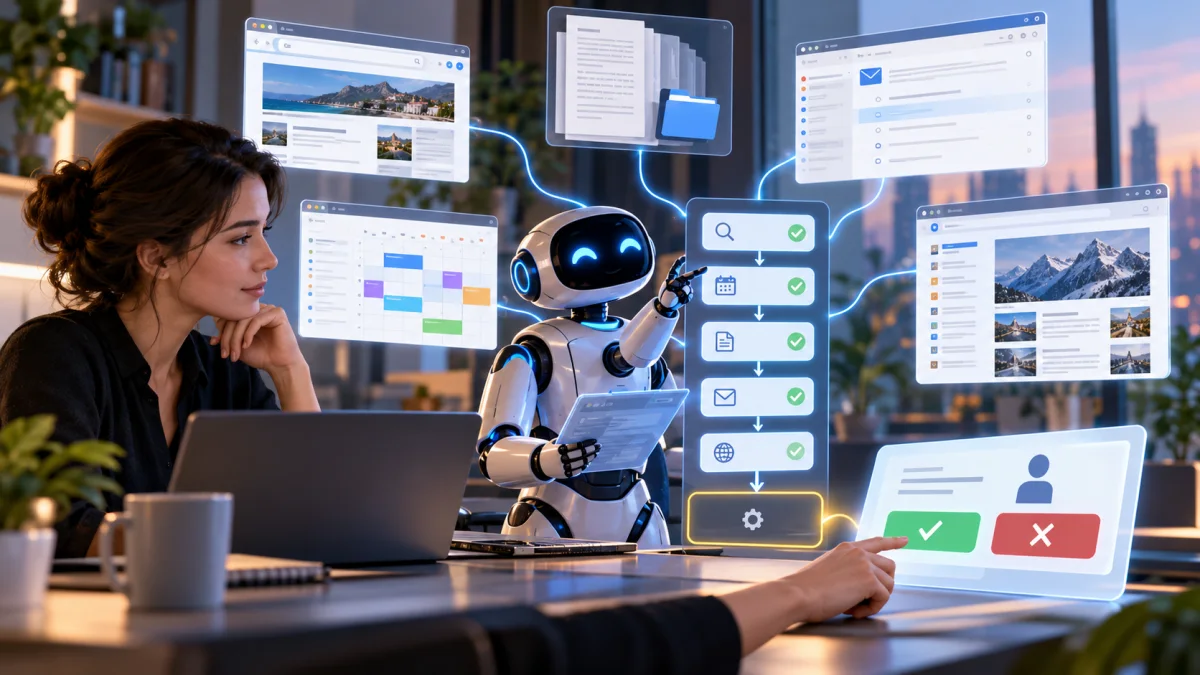
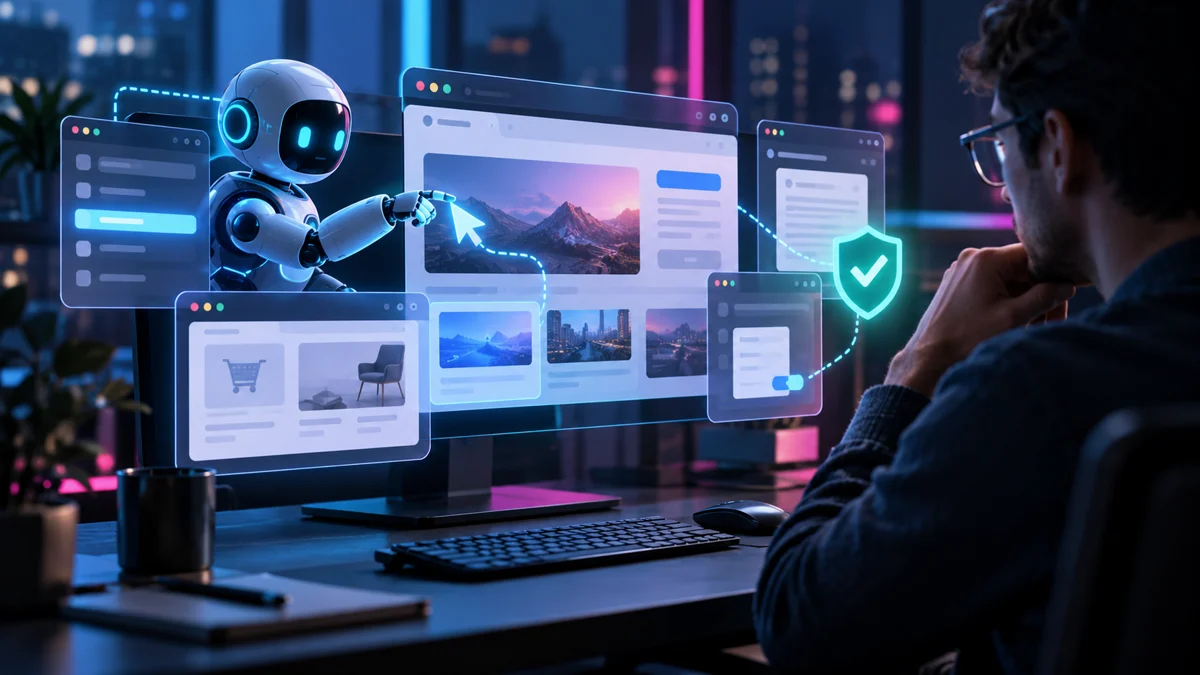
An AI agent is a software system that can pursue a goal through multiple steps instead of replying with one isolated message. It may decide what information to collect, call a search or business API, inspect the result, revise its plan and ask a person to approve an important action. The word “autonomous” should not be interpreted as “always correct.” A useful agent is one that acts within clear permissions and makes its reasoning, evidence and failures visible enough for people to supervise.
For related updates, explore Tech News, Mobile Phones, Startup News and Knowledge Base for more information.
How an AI agent works
A typical agent loop starts with a goal and constraints. The model then creates a plan, selects a tool, sends a structured request, receives an observation and decides what to do next. The loop can stop when the task is complete, when a confidence rule fails or when human approval is required. Some systems also use separate agents for research, coding, testing or review, but adding more agents does not automatically improve quality.
Examples of useful agent workflows
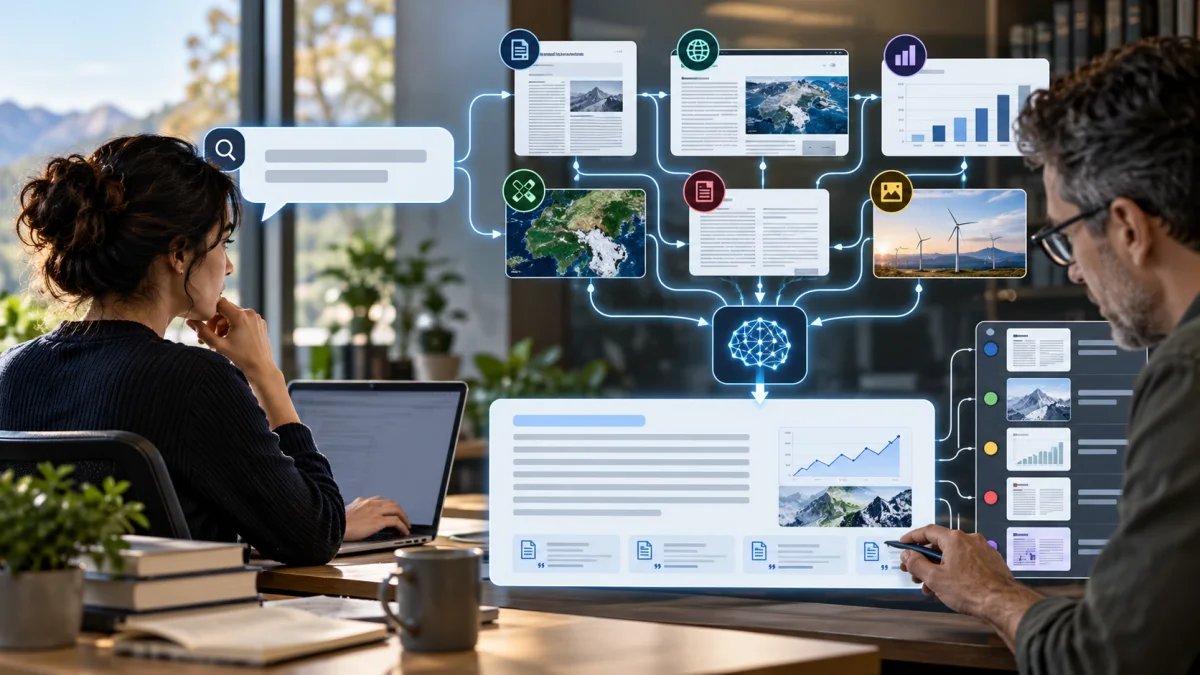
- Research: collect official sources, compare them and prepare a cited briefing.
- Customer support: classify a request, retrieve account information and draft a response for approval.
- Software: inspect a repository, propose a patch, run tests and summarise the result.
- Operations: read a form, validate fields and create a task in an approved business system.
- Personal productivity: organise notes, prepare a schedule or turn a meeting transcript into action items.
Why agents are difficult to trust
An agent can make a wrong plan, misunderstand an instruction or trust an unverified web page. Prompt injection is especially important: hostile text inside a document, web page or email may attempt to change the agent's instructions. An agent may also expose private data through a tool call, send an incorrect email or make a duplicate transaction. Long tasks increase the chance that a small early mistake will compound into a large final error.
A safer agent architecture
- Use least-privilege access and separate read-only tools from write actions.
- Place sensitive actions behind explicit human approval or a transaction limit.
- Run untrusted browsing and code in a sandbox with network and file restrictions.
- Log prompts, tool calls, observations, approvals and final outcomes for review.
- Validate tool inputs and outputs with deterministic rules wherever possible.
- Give the agent a stop button, timeout and rollback path.
What businesses should measure
Agent quality should be measured with task completion rate, factual accuracy, unsafe-action rate, escalation rate, latency and total cost. A workflow that completes 90 percent of tasks but creates a costly error in the remaining 10 percent may not be ready for unattended operation. Start with low-risk internal tasks, collect failures and expand permissions gradually.
Source: OpenAI: Introducing the Agents API
Source: Anthropic: Framework for safe and trustworthy agents
Source: Anthropic: Measuring AI Agent Autonomy
Important: AI tools, features, prices and availability change quickly. Verify current product documentation, privacy terms, copyright rules and safety controls before using an AI system for important work.
Conclusion
Review the official sources, dates and eligibility conditions mentioned in this article before taking action. For more related updates, explore the category links above.
FAQs
What is this article about?
Learn how AI agents plan tasks, use tools, inspect results and request approval, plus the main risks and a safe deployment checklist.
What topics are covered in this article?
This guide covers: How an AI agent works, Examples of useful agent workflows, Why agents are difficult to trust, A safer agent architecture, What businesses should measure.
What should readers compare before choosing a product?
Compare the specifications, price, software support, camera, battery, warranty and availability before making a purchase decision.
When was this article last updated?
This article was last updated on 17 October, 2026. Always verify deadline-sensitive information from the official source linked in the article.
Comments (0)
No Comments Found